Chat with AI Agent, powered by Text

Production-Grade Hardened Images Without CVE Debt

Tick icon
Near-zero CVEs at the foundation
Tick icon
STIG and CIS hardened with FIPS crypto
Tick icon
Same distros and tags with zero refactoring
secure-banner-img
secure-risk-img

Your Base Image Determines Most of Your Risk

Removes entire vulnerable code paths, lowering CVE exposure up to 99.9%.

Blue hexagonal secure shield icon with a closed dot in top left and a ringed dot in bottom right inside the shape.
Most vulnerabilities originate in the operating system layer
Blue hexagonal secure shield icon with a closed dot in top left and a ringed dot in bottom right inside the shape.
Inherited CVEs propagate across every service built on top
Blue hexagonal secure shield icon with a closed dot in top left and a ringed dot in bottom right inside the shape.
Weak foundations create downstream security and audit failures

Continuous Elimination That Produces Defensible Results

Assurance icon new

Public Images

Community-maintained, general purpose base images.

Tick Icon
High and unpredictable CVE counts
Tick Icon
No compliance-aligned hardening
Tick Icon
Unknown build provenance
assurance-icon-new

Proprietary Images

Standardized, open, and ultra-secure.

Tick Icon
Closed ecosystems and limited transparency
Tick Icon
Opaque patching and dependency chains
Tick Icon
Long-term vendor lock-in risk
assurance-icon-new

RapidFort Curated Images

Standardized, open, and ultra-secure.

Tick Icon
Near-zero CVEs with continuous rebuilds
Tick Icon
STIG and CIS aligned under NIST guidance
Tick Icon
Open, transparent, LTS Linux distribution

Recommended for Enterprise

Hardened Continuously and Verified Transparently

BG Card
Daily Cadence
verify-icon

Deterministic Build

Deterministic builds with pinned dependencies

BG Card
NIST Certified
verify-icon

Hardening Engine

Predictable patch cadence for critical and full rebuilds

BG Card
SPDX / CycloneDX
verify-icon

FIPS Validation

Embedded FIPS 140 validated cryptographic modules

BG Card
Production Ready
verify-icon

SBOM Generation

SBOM generated for every image build

Standard Patch Cadence

Predictable Security Response

24h

Critical Fix Time

7d

Standard Rebuild

0

Refactor Required

Adopt Secure Images Instantly

01

Select Base

Select a curated LTS Linux image

02

Swap Tag

Swap the image tag in your build

03

Deploy

Build and deploy using existing pipelines

04

Automate

Receive continuous hardened updates automatically

arrow
arrow
arrow
rocket icon

No Code Changes

Environment variables and paths remain identical.

lightning icon

No Pipeline Refactoring

Compatible with Jenkins, GitLab, GitHub Actions.

secure icon

No Workflow Disruption

Standardizes security across the entire org.

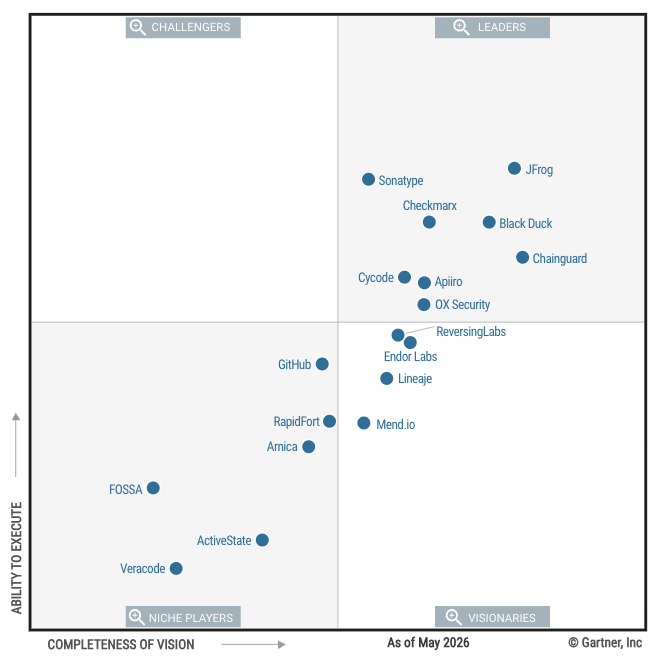
Ability to Execute

2026 Gartner® Magic Quadrant™

for Software Supply Chain Security

Get the Report